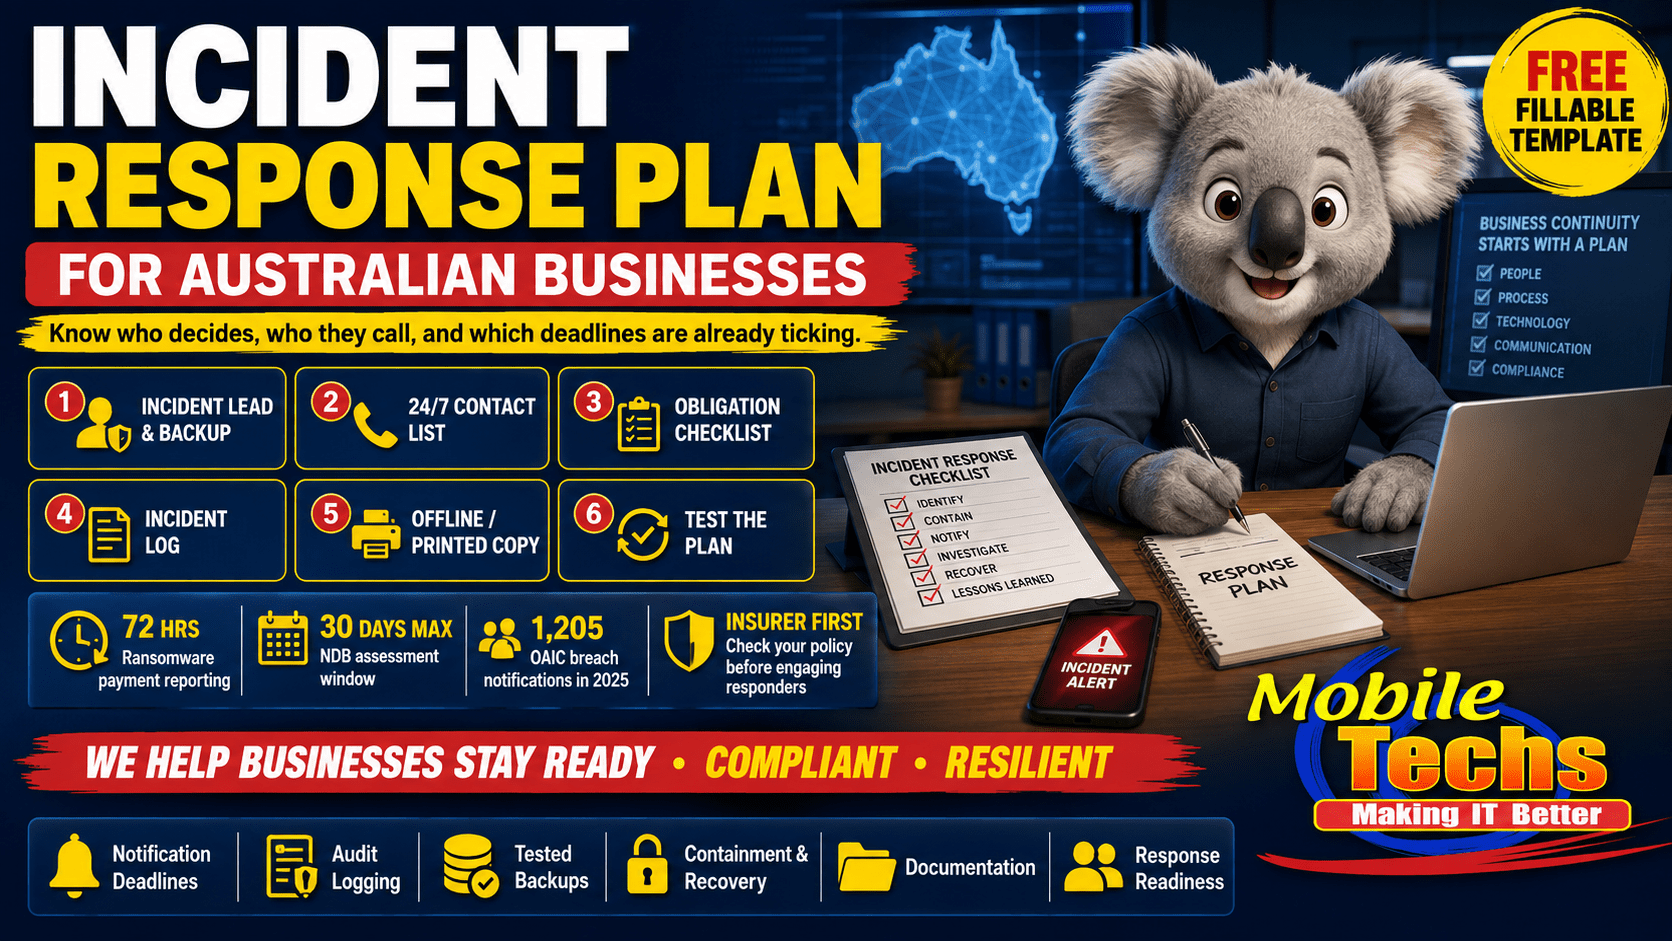
Does Your Business Need an Incident Response Plan? (With Free Fillable Template)
There is no single law that says "you must have an incident response plan" — but between the NDB scheme, the Cyber Security Act's...
There is no single law that says "you must have an incident response plan" — but between the NDB scheme, the Cyber Security Act's...
Tranche 2 AML/CTF, the TPB Code Determination and record data breach numbers have made an accounting practice's technology stack a regulated object — and...
Tranche 2 AML/CTF obligations, record data breach numbers and new court protocols on AI have made a law firm's technology stack a regulated object....
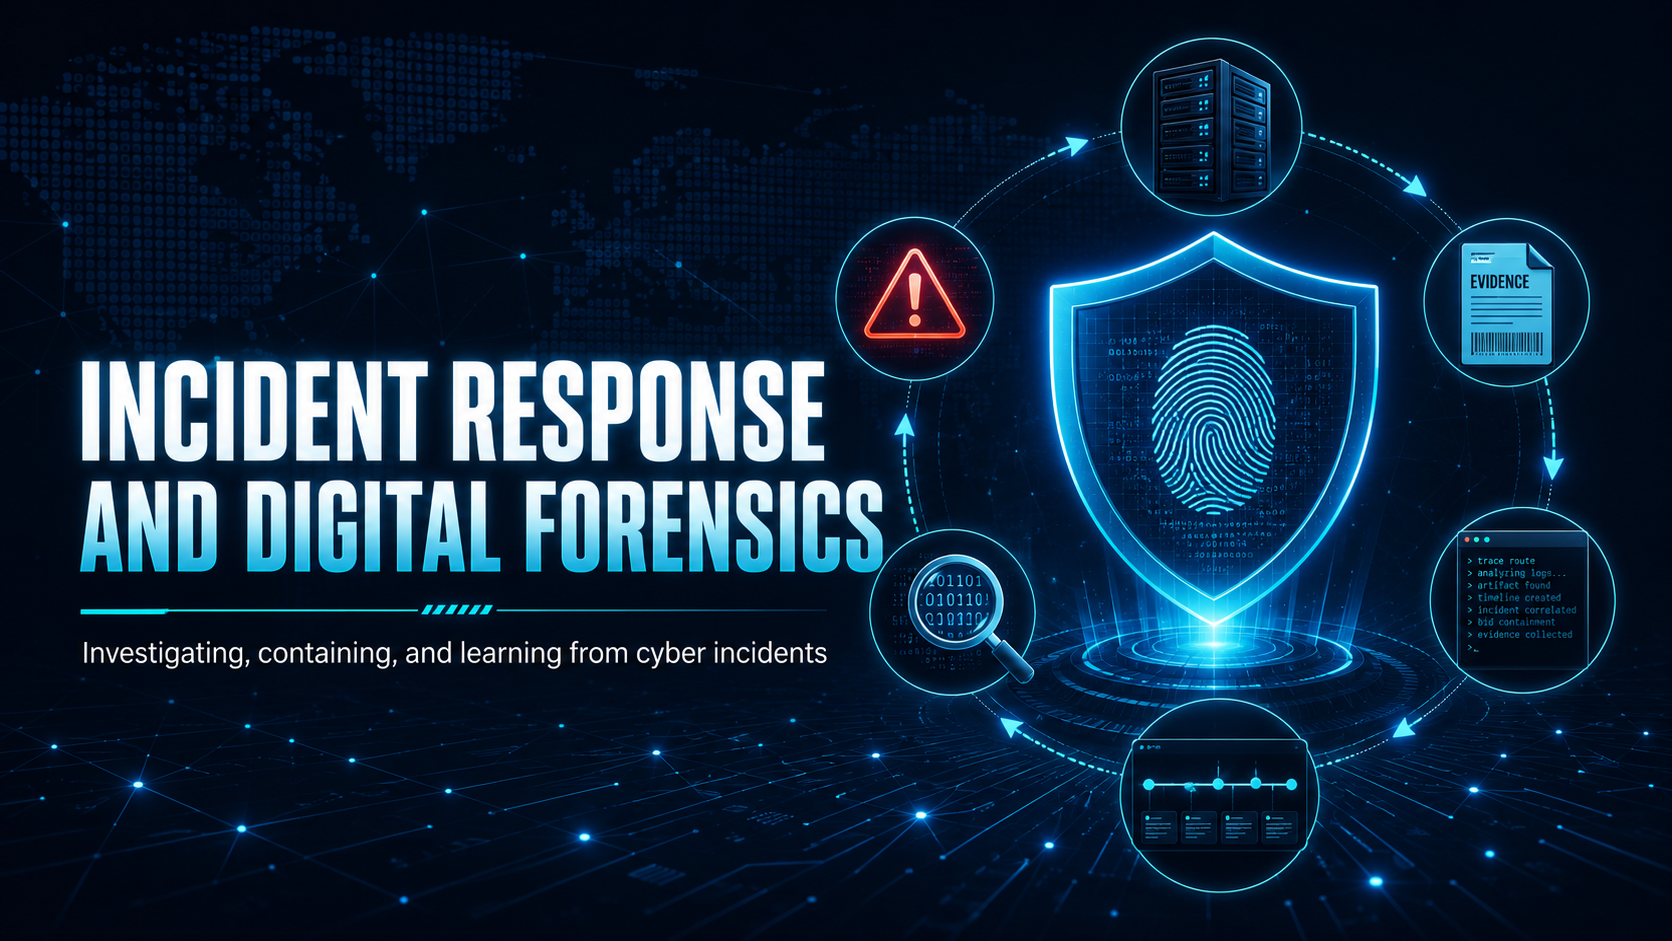
The six-phase incident response lifecycle — prepare, identify, contain, eradicate, recover, learn — plus evidence preservation and chain-of-custody basics for a calm, effective response.
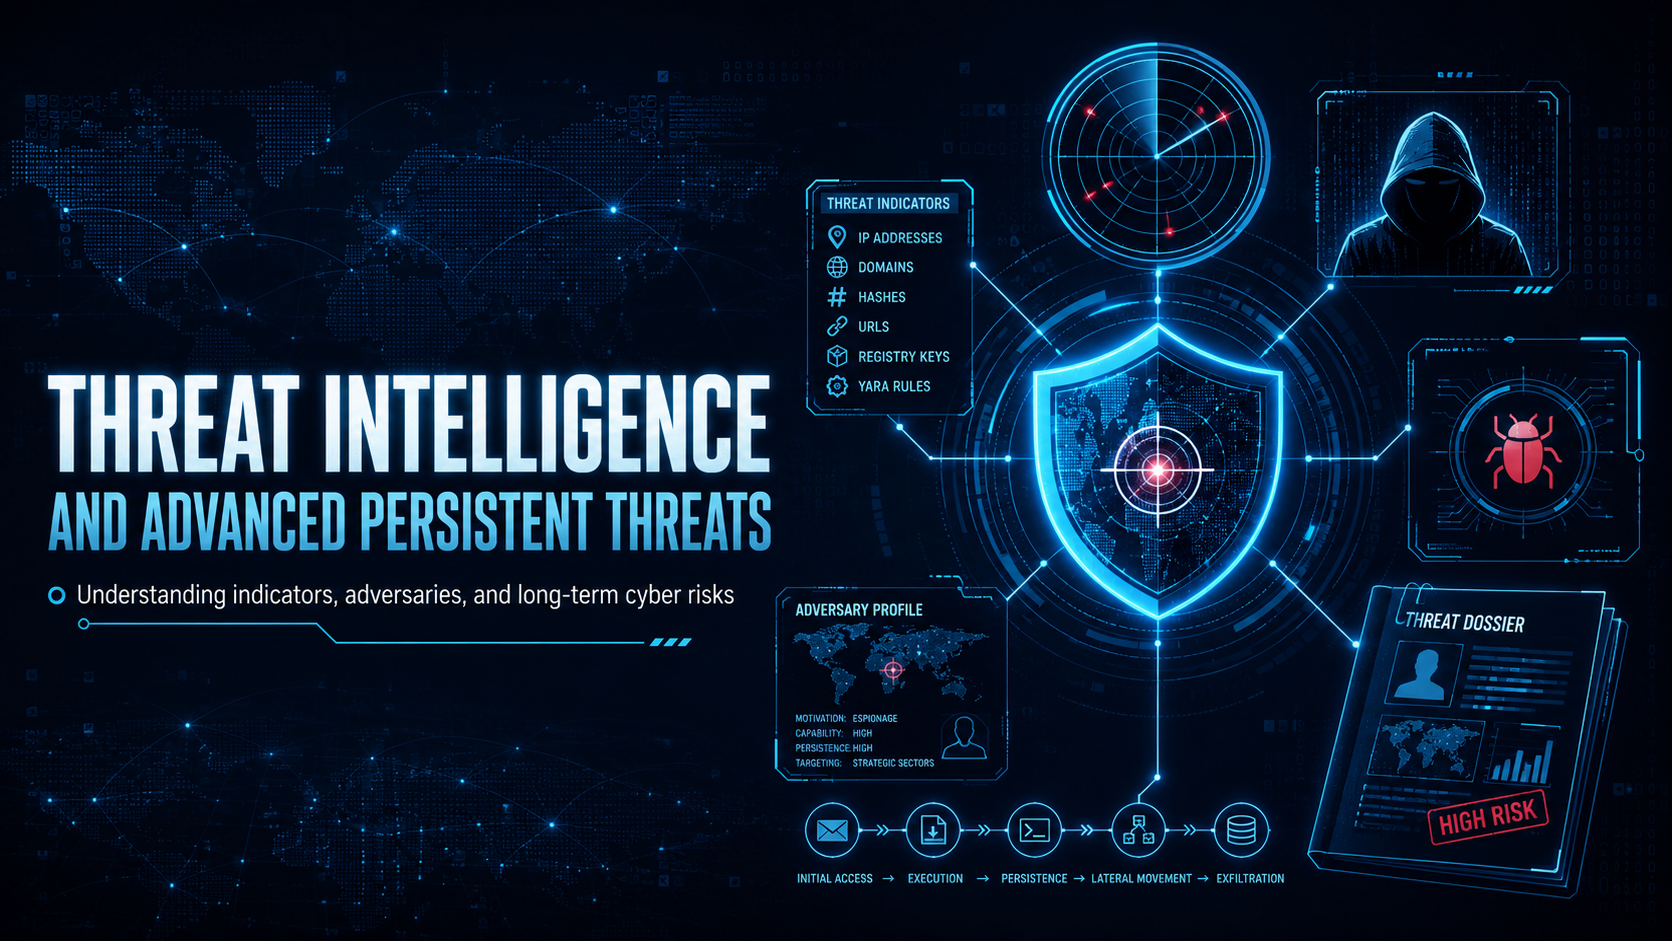
How nation-state advanced persistent threats, cybercriminals, hacktivists and insiders operate, how threat intelligence informs defence, and how MITRE ATT&CK maps attacker behaviour end to...
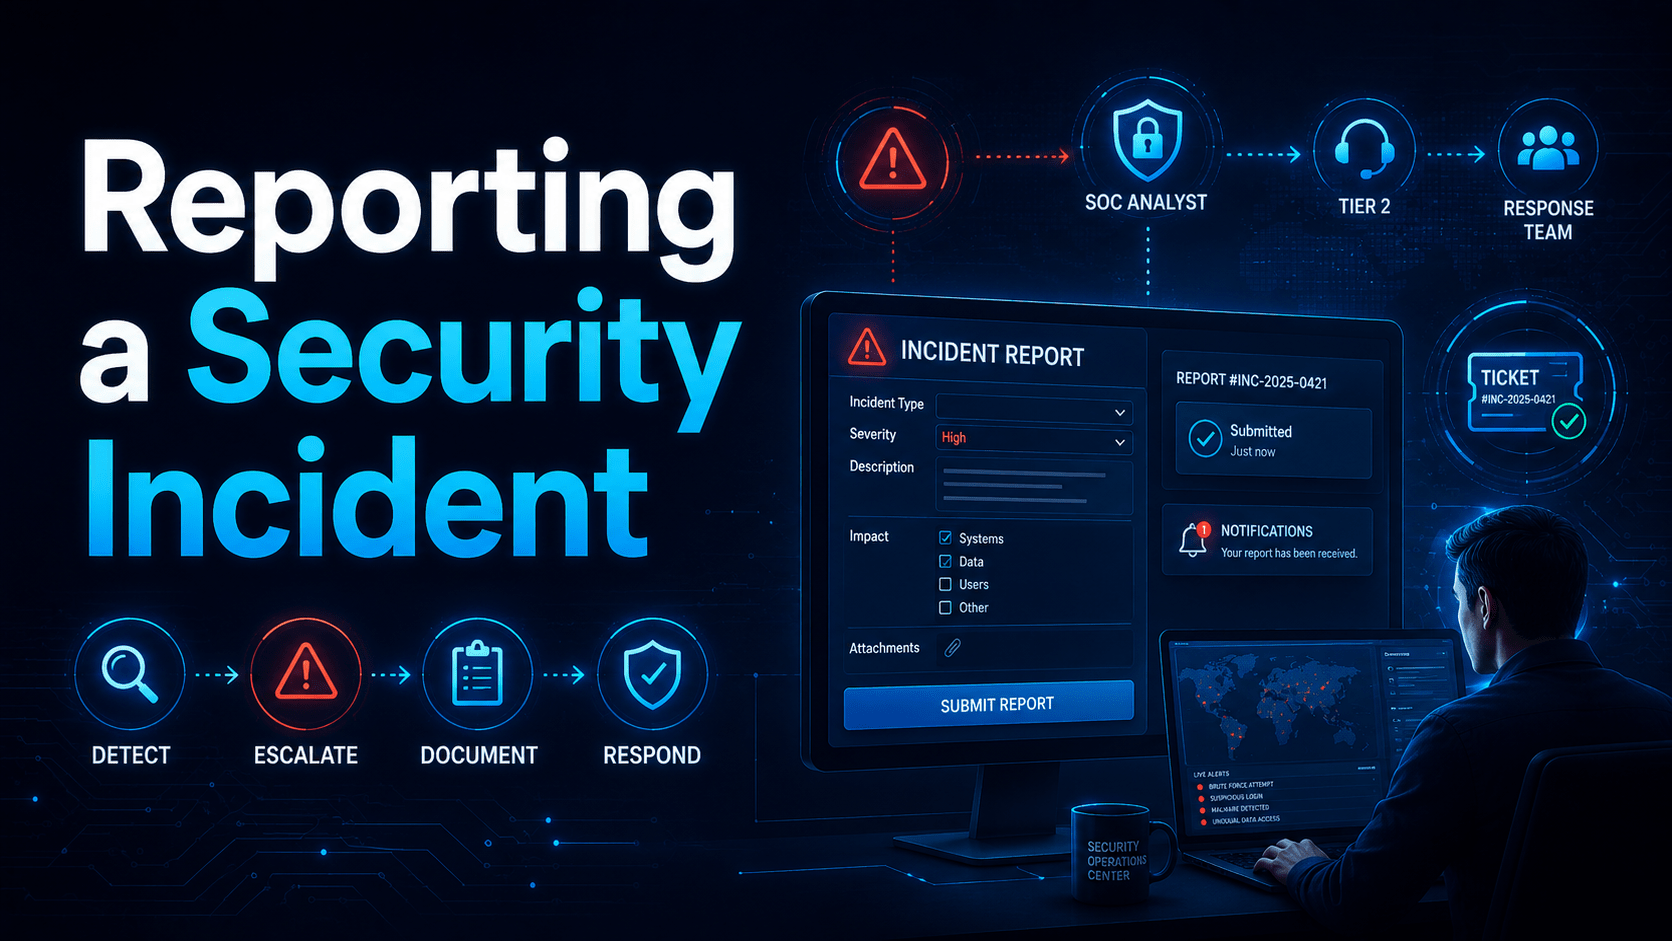
Early reporting is the single biggest factor in limiting damage from a cyber incident. What actually counts as an incident, why speed beats certainty,...
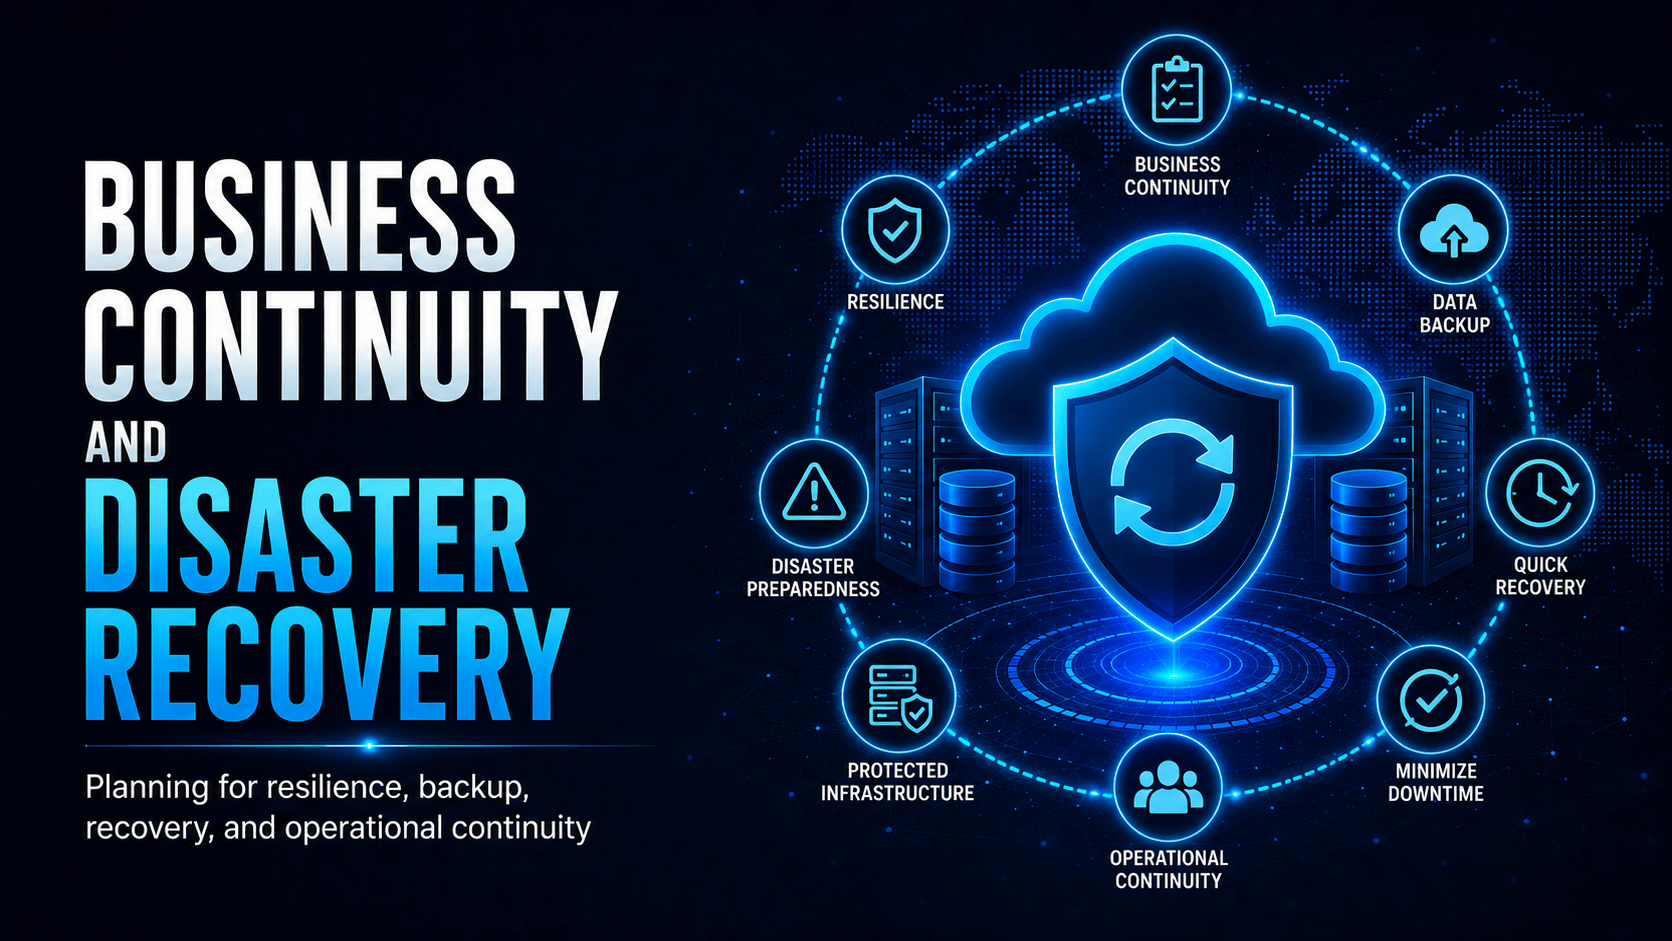
How to plan for and recover from major disruptions — from ransomware to floods — with clear RTO and RPO targets, tested backups and...