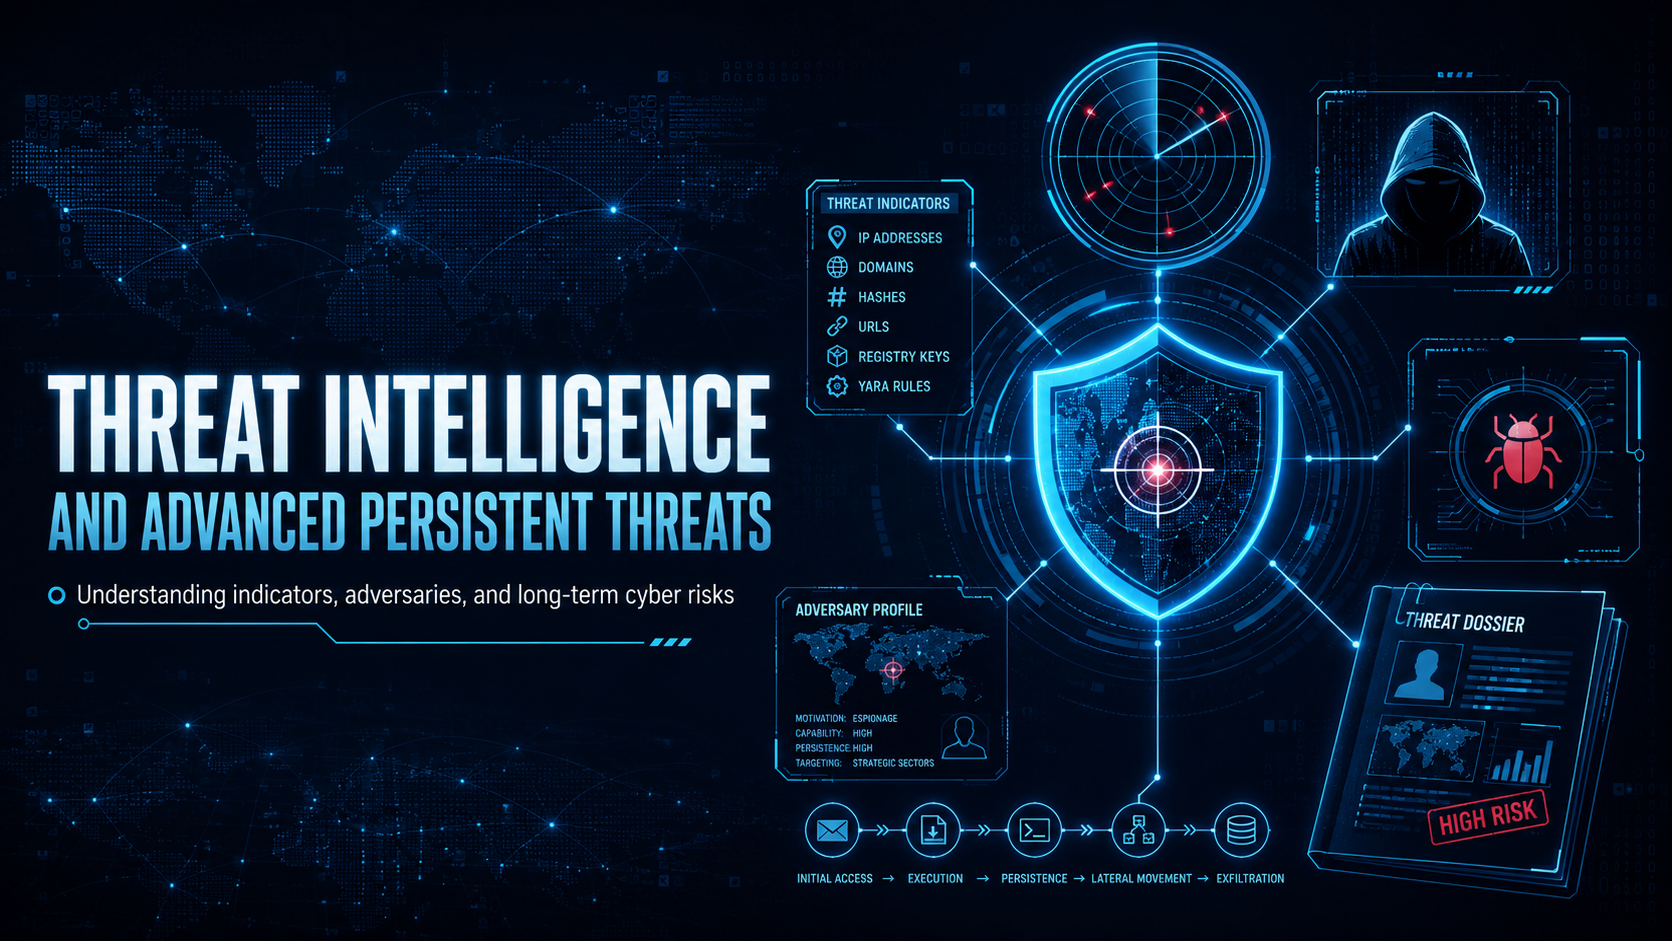
Threat Intelligence and Advanced Persistent Threats
How nation-state advanced persistent threats, cybercriminals, hacktivists and insiders operate, how threat intelligence informs defence, and how MITRE ATT&CK maps attacker behaviour end to...
How nation-state advanced persistent threats, cybercriminals, hacktivists and insiders operate, how threat intelligence informs defence, and how MITRE ATT&CK maps attacker behaviour end to...
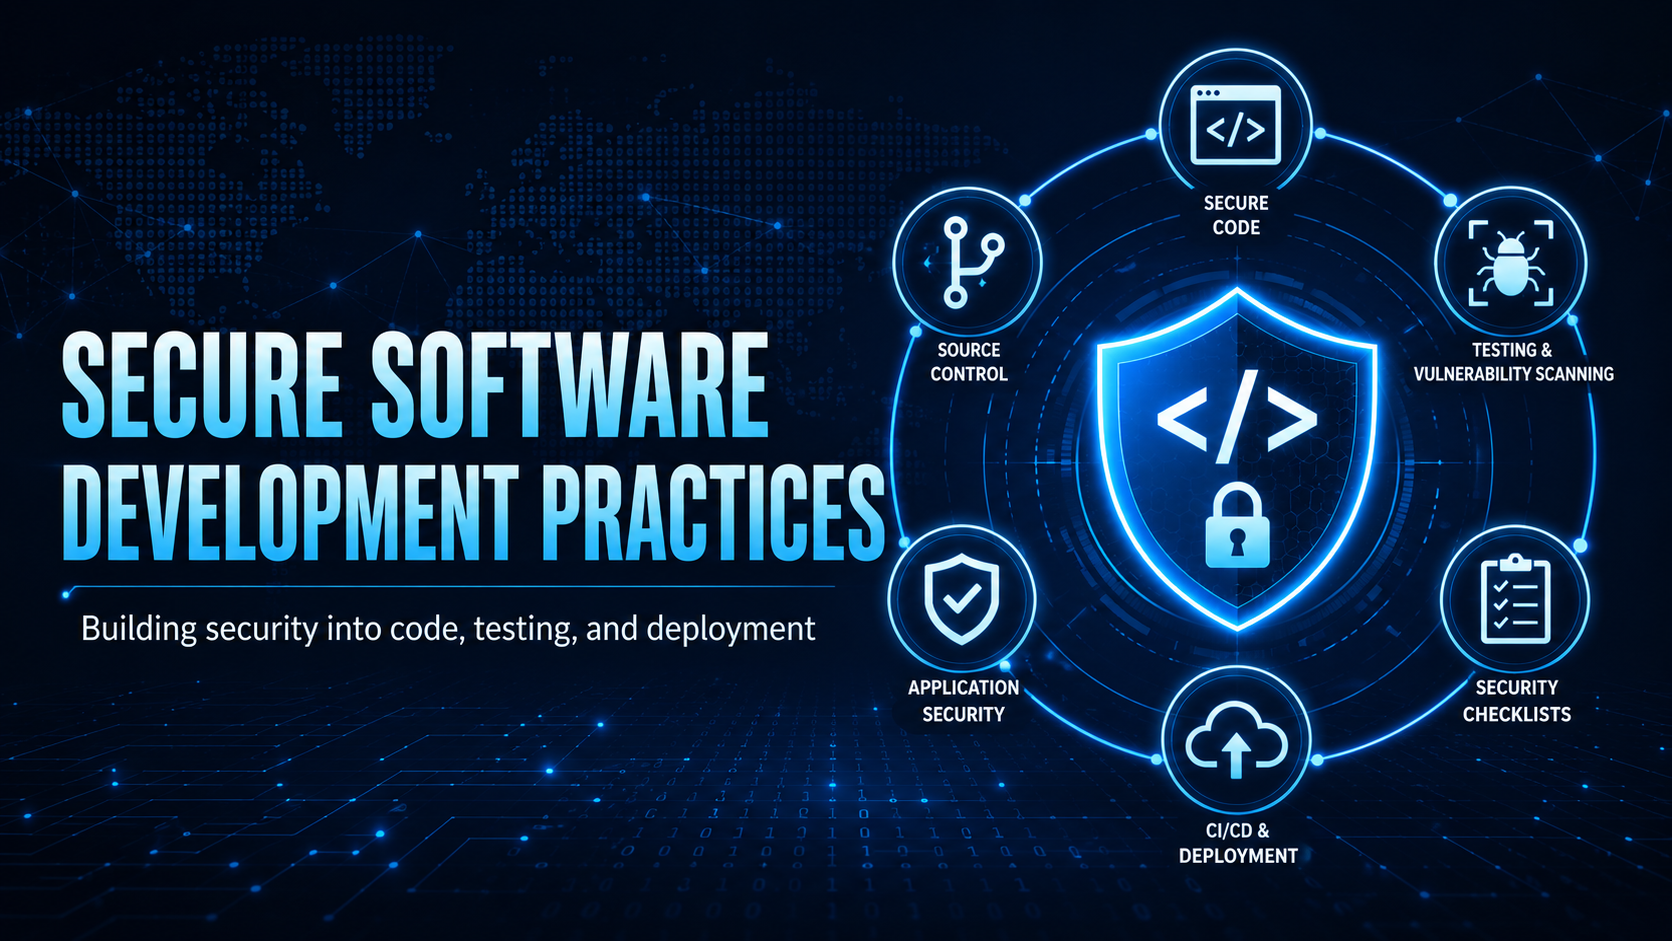
The OWASP Top 10, shift-left thinking, secure coding practices — why building security into software from day one costs a fraction of trying to...
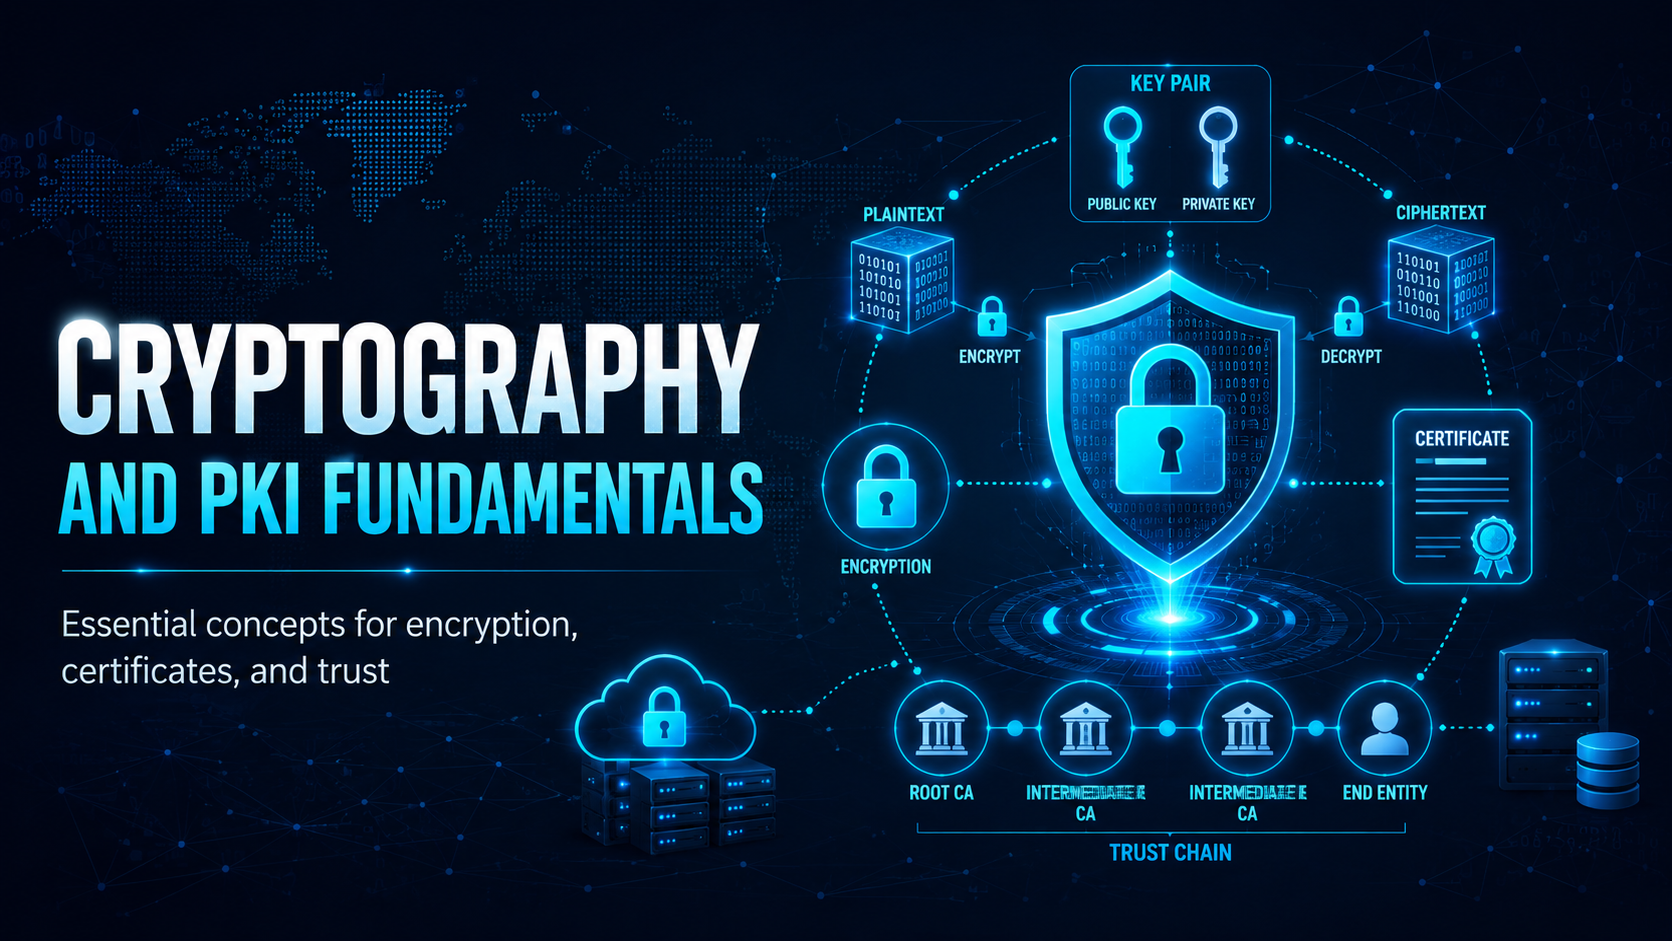
The essentials of modern cryptography in plain English: symmetric vs asymmetric encryption (AES, RSA), hashing, digital signatures, TLS and PKI — and where each...
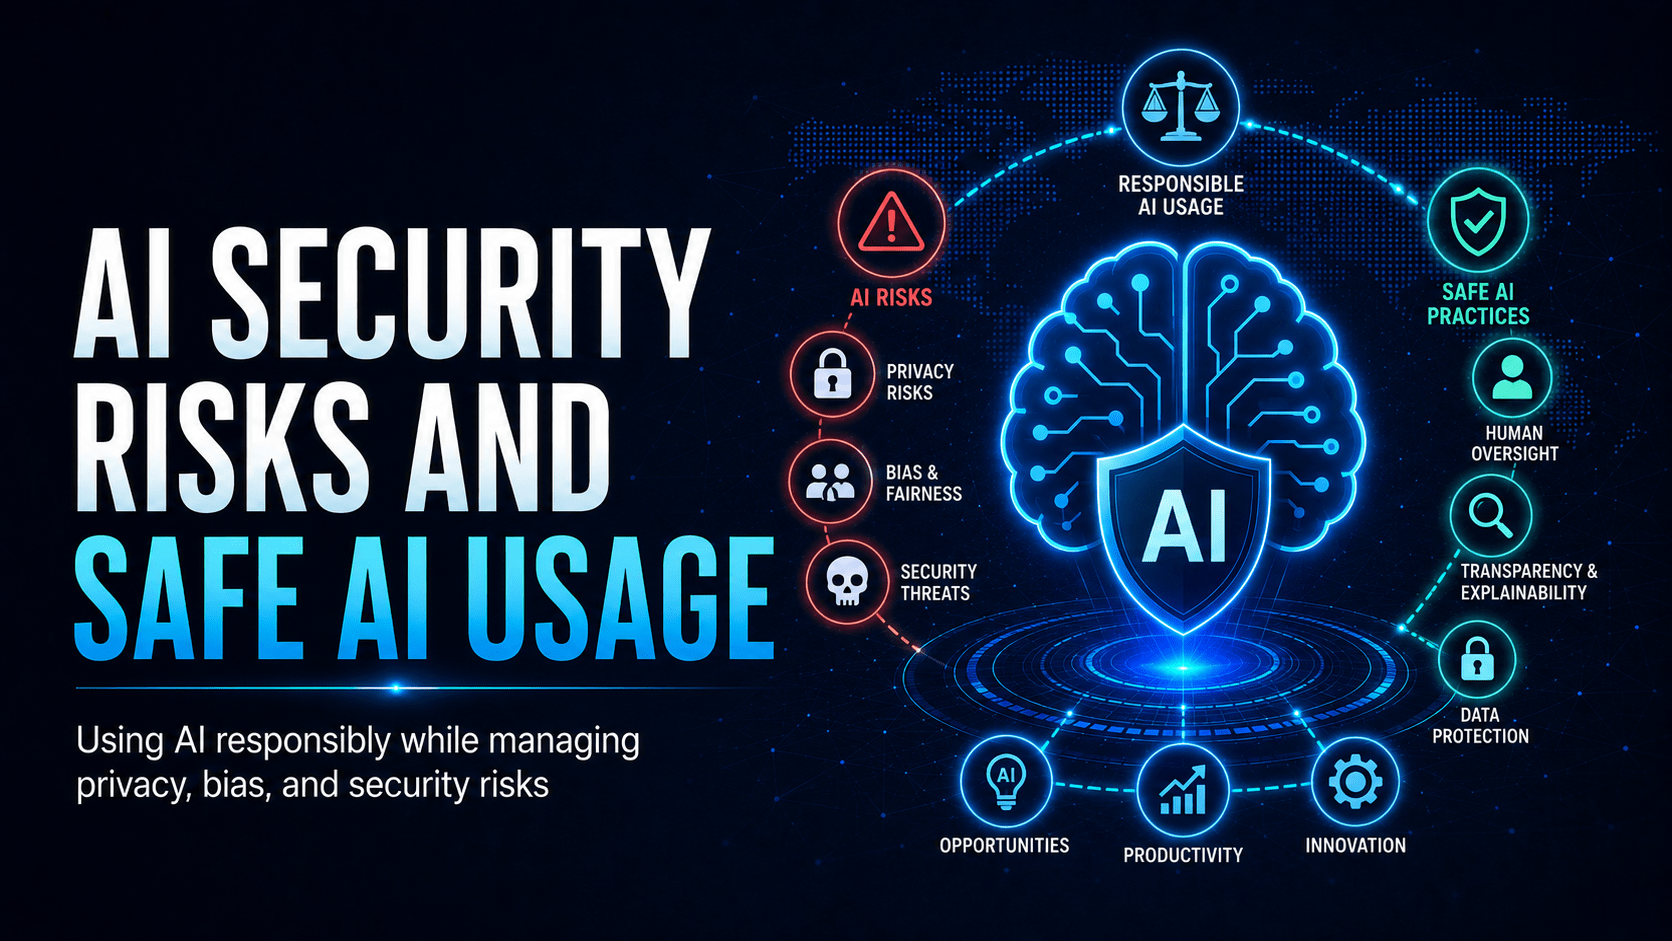
AI tools like ChatGPT, Microsoft Copilot and Google Gemini are transforming work — and introducing new risks. How to use them safely, and how...
Business Email Compromise is one of the most financially damaging cyber crimes going. How BEC attacks use email impersonation and social engineering to redirect...
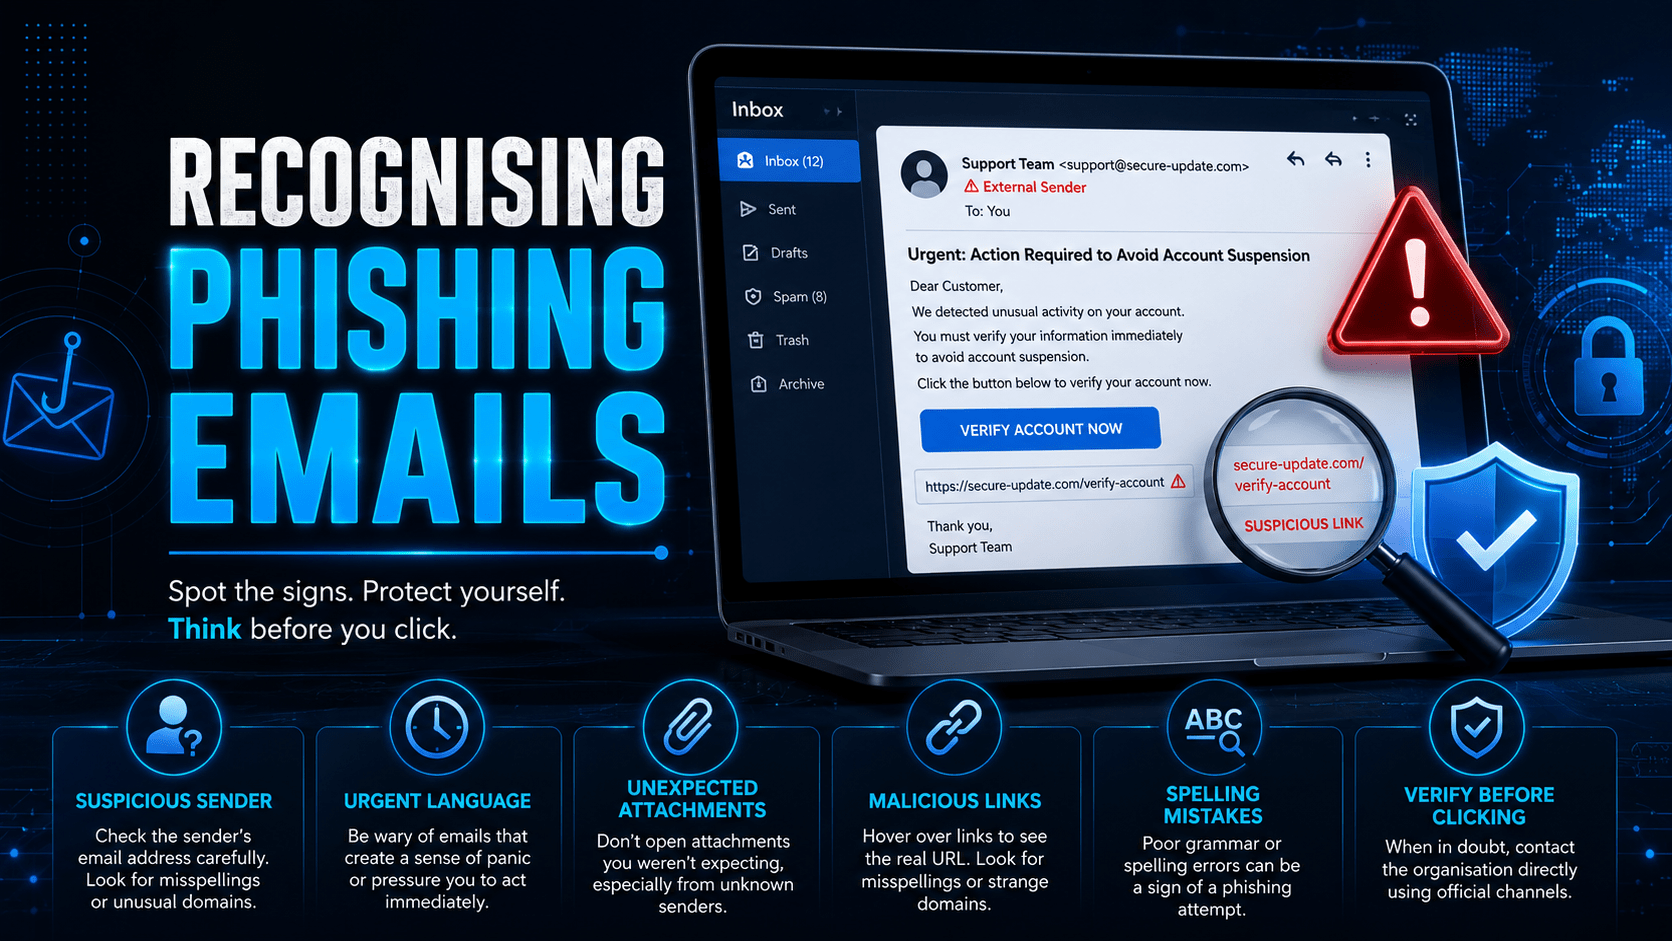
Phishing is the most common entry point for cyberattacks worldwide. How to spot the warning signs — mismatched sender addresses, dodgy links, urgency, unusual...
USB drives and removable media are one of the most overlooked risks in the workplace. Why a 'found' USB should never be plugged in,...
Passwords are the first line of defence on every account you hold. Why weak and reused passwords cause most compromises, how to build strong...
QR code phishing — 'quishing' — bypasses traditional email security by hiding a malicious URL inside a QR image. How the attack works, why...